Privacy & Compliance · 9.3
Information Security Management Support
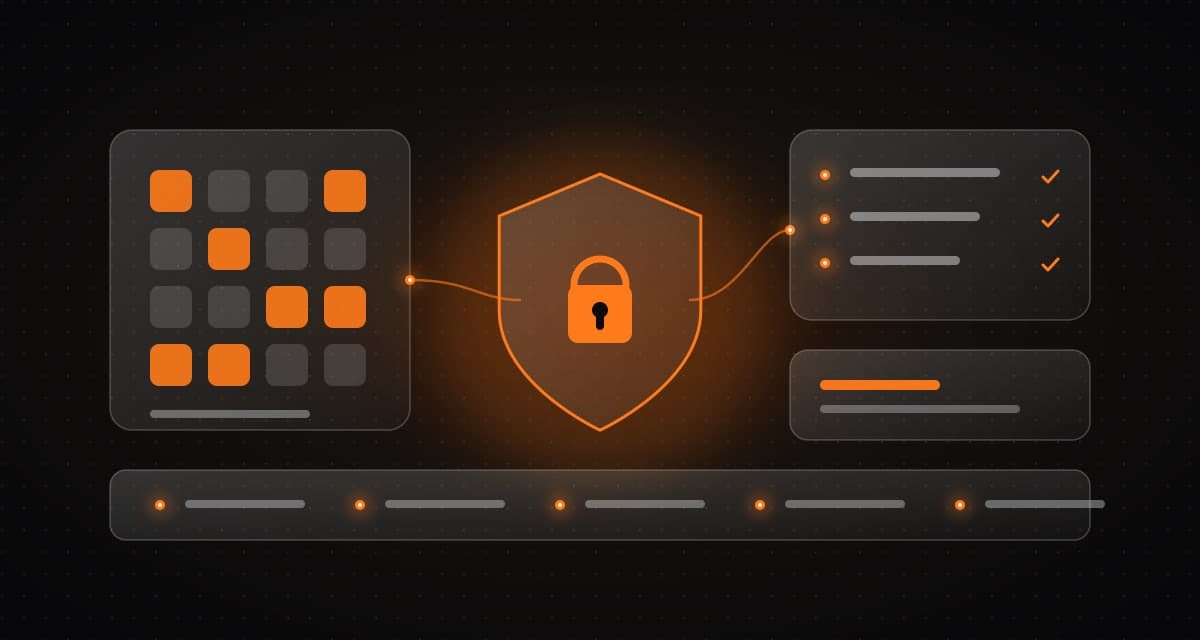
We help document security policies, asset and risk registers, access processes, incident procedures, supplier reviews, and evidence collection.
What it is and how it works
We help document security policies, asset and risk registers, access processes, incident procedures, supplier reviews, and evidence collection.
Who it is for
Teams building documented security practices, possibly ahead of a formal assessment.
What is typically included
- Security policies and risk registers
- Asset and access processes
- Incident procedures and supplier reviews
- Evidence collection
Client benefit
Structured controls improve consistency and may support preparation for formal assessment.
Keep in mind
Support must not be described as certification unless formally awarded.
Typical deliverables
The final list depends on discovery and the scope we agree together.
- 01
Documented policies and registers
- 02
Process and evidence templates
- 03
Readiness notes
How we deliver
- Step 1
Discover
Map the workflow, data, risks and constraints before any design work starts.
- Step 2
Architect
Define the system, integrations and human-approval points as a reviewable design.
- Step 3
Build
Deliver a practical first slice, then extend it in small, tested increments.
- Step 4
Operate
Monitor, secure and continuously improve the system after launch.
Common questions
Do you certify us?
No. This support must not be described as certification unless formally awarded by a certifying body.
Can it help prepare for an audit?
Structured controls improve consistency and may support preparation for formal assessment.
Next
Talk through your system with our engineers.
Share the problem and constraints. We will map relevant capabilities to your goals, existing systems and timeline, then define scope and measurable outcomes.